Intern Training
October 22, 2026
October 22, 2026
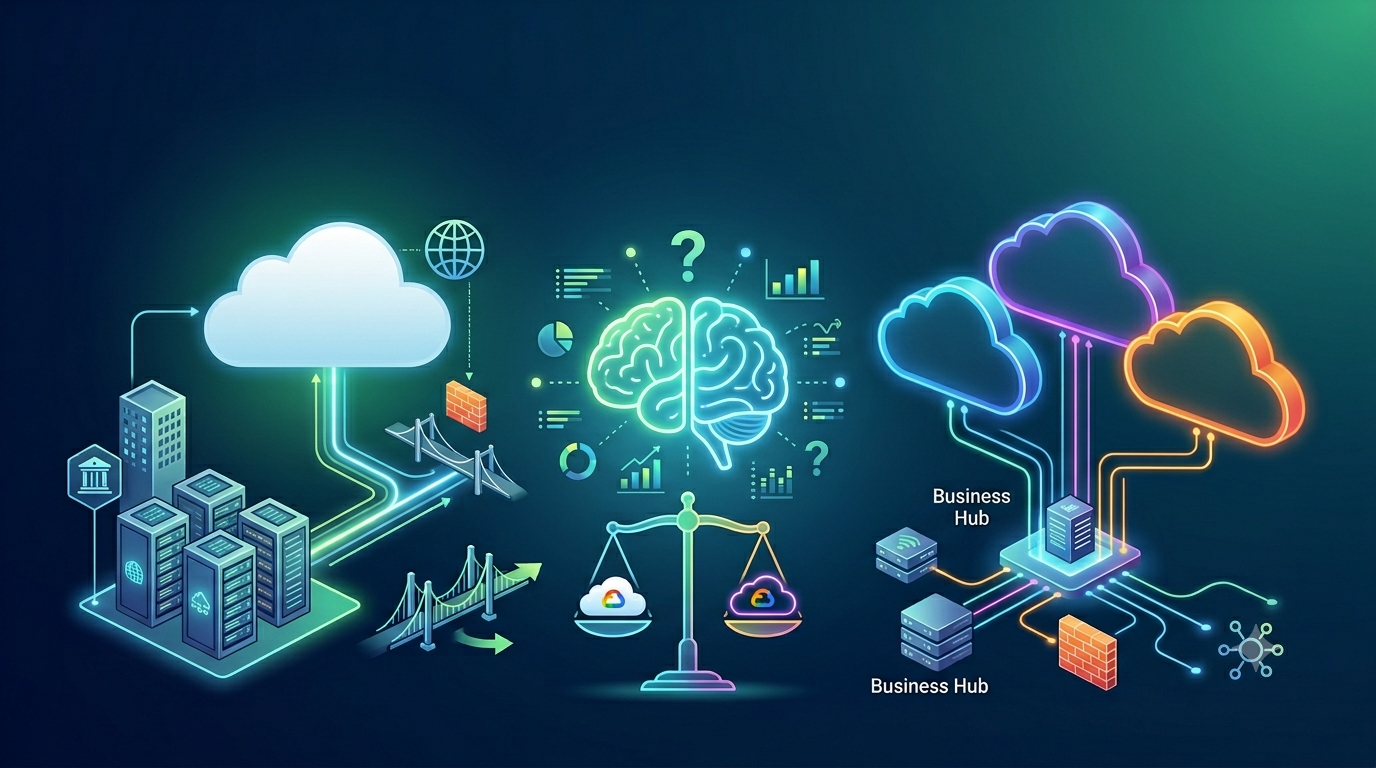
Using AWS, Azure, and Google Cloud together can give organizations more flexibility. One team may run applications on AWS, another may use Azure because of its Microsoft ecosystem, while data and AI workloads may sit on Google Cloud.
The problem starts when each cloud becomes its own operational island.
Different dashboards. Different IAM models. Different networking concepts. Different billing systems. Different security policies. Different monitoring tools.
At that point, having three cloud providers can start to feel like having three separate IT environments.
Multi-cloud management is about bringing those environments under a consistent operating model without pretending that AWS, Azure, and GCP work the same way.
The goal is not to make every cloud identical. It is to establish common standards for visibility, security, governance, cost, identity, networking, and operations while still using each provider’s native capabilities where they make sense.
Multi-cloud management is the process of operating workloads across two or more cloud providers using common policies, processes, visibility, and operational controls.
For an organization using AWS, Azure, and GCP, this typically means managing:
The important distinction is that multi-cloud management does not mean managing all three clouds from one dashboard.
A dashboard can provide visibility, but effective management requires consistent processes behind it.
AWS itself describes multicloud management in terms of centralizing observability, management, and configuration across AWS and other cloud providers. Microsoft provides guidance for unified hybrid and multicloud operations, while Google Cloud provides tooling for managing resources and Kubernetes environments across clouds.
The three clouds offer similar categories of services, but their implementations differ.
| Area | AWS | Azure | GCP |
| Compute | EC2 | Virtual Machines | Compute Engine |
| Object storage | S3 | Blob Storage | Cloud Storage |
| Kubernetes | EKS | AKS | GKE |
| Identity | IAM | Microsoft Entra ID / Azure RBAC | Cloud IAM |
| Network | VPC | Virtual Network | VPC |
| Organization | Organizations / Accounts | Management Groups / Subscriptions | Organization / Folders / Projects |
| Monitoring | CloudWatch | Azure Monitor | Cloud Monitoring |
| Security posture | AWS security services | Defender for Cloud | Security Command Center |
| Cost management | AWS Cost Management | Azure Cost Management | Cloud Billing |
The names may look different, but the bigger problem is that the underlying concepts and management models are also different.
For example, an IAM policy written for AWS cannot simply be copied into Azure or GCP.
The answer is therefore not to force the platforms into identical configurations. Instead, define what the organization requires and then implement the appropriate control in each cloud.
A reliable multi-cloud operating model should cover six areas:
Visibility → Identity → Security → Governance → Cost → Operations
If one of these is missing, management becomes fragmented.
The first question should be:
“What are we actually running across all three clouds?”
You need visibility into:
Without a complete inventory, it becomes difficult to answer basic management questions.
For example:
How many production databases do we have across AWS, Azure, and GCP?
Which resources have public exposure?
Which accounts or projects contain sensitive data?
Which workloads are consuming the most money?
Who has administrative access?
A centralized inventory does not necessarily mean replacing every native cloud console. It means having an organization-wide source of truth that brings the environments together.
Identity is one of the biggest challenges in multi-cloud environments.
AWS uses IAM. Azure integrates deeply with Microsoft Entra ID and Azure RBAC. GCP uses Cloud IAM.
Instead of allowing every cloud to develop its own independent identity model, establish common organizational principles.
For example:
The exact implementation can differ between providers.
The policy should not.
For example:
Organization policy: Production administrators require strong authentication and privileged access controls.
AWS implementation: IAM roles and federation.
Azure implementation: Microsoft Entra ID and Azure RBAC.
GCP implementation: Cloud IAM and federation.
This distinction is important.
Standardize the security requirement, not necessarily the underlying cloud configuration.
AWS guidance has also highlighted the importance of consistent authentication and authorization mechanisms when applications span multiple cloud environments.
Multi-cloud security becomes difficult when every provider has different security expectations.
Define a common baseline first.
For example:
| Security Area | Organization Standard |
| Authentication | MFA required |
| Privileged access | Restricted and monitored |
| Network exposure | No unnecessary public access |
| Encryption | Required for sensitive data |
| Logging | Enabled for critical activity |
| Vulnerability management | Regular assessment |
| Backups | Defined by workload criticality |
| Secrets | Centralized and protected |
| Security alerts | Centralized monitoring |
| Compliance | Policy mapped to required frameworks |
Then map those requirements to AWS, Azure, and GCP.
This is much more scalable than creating completely separate security policies for each cloud.
Multi-cloud security platforms can also provide centralized posture visibility. For example, Microsoft Defender for Cloud currently supports multicloud posture management across AWS and GCP in addition to Azure, while its June 2026 expansion added broader AWS and GCP resource coverage.
However, centralized tooling should complement—not replace—native cloud security controls.
Governance answers a different question from security.
Security asks:
“Is this environment protected?”
Governance asks:
“Are teams using the environment in the way the organization has approved?”
Create policies for:
For example:
Every production resource should have:
Environment = Production
Owner = Application Team
Application = Customer Portal
BusinessUnit = Finance
CostCenter = FIN-001
The exact tagging syntax can differ between AWS, Azure, and GCP. The organizational requirement should remain consistent.
Cloud cost management becomes significantly harder when billing information exists in three different systems.
AWS reports costs through AWS billing and cost management tools.
Azure has Azure Cost Management.
GCP uses Cloud Billing.
The challenge is not simply seeing the individual bills.
It is answering:
“How much are we spending on this application across all clouds?”
To answer that, normalize cost data into common dimensions such as:
Then track:
A recent AWS-published case study on multi-cloud FinOps illustrates the value of normalizing cost data across cloud providers to reduce manual consolidation and identify savings opportunities.
The objective is not necessarily to make AWS, Azure, and GCP cost the same.
It is to understand why costs differ and whether each workload is running economically.
Each cloud has its own monitoring platform.
That is useful for cloud-specific troubleshooting, but it can become difficult for an operations team responsible for the entire environment.
You need a common operational view of:
A common observability layer should answer:
“Is the application working?”
rather than:
“Is the AWS server working?”
Those are different questions.
For example, an application could have healthy EC2 instances while its Azure-hosted dependency is unavailable.
Multi-cloud monitoring therefore needs to follow the application and business service, not just the infrastructure provider.
AWS has also documented the operational challenge of observing and managing applications and infrastructure across multiple clouds and recommends consistent tooling for visualization and automation.
Configuration drift is one of the biggest operational risks in multi-cloud environments.
Suppose a security requirement says:
Production storage must not be publicly accessible.
A team may configure that correctly in AWS but forget to apply the equivalent control in Azure or GCP.
Infrastructure as Code can reduce this risk by making infrastructure configuration repeatable and reviewable.
Tools such as Terraform can help teams define infrastructure consistently across providers.
A typical workflow looks like:
Infrastructure Requirement
↓
Infrastructure as Code
↓
AWS / Azure / GCP
↓
Automated Validation
↓
Monitoring
↓
Drift Detection
The objective is not to create one giant configuration that hides all cloud-specific differences.
Instead, create reusable standards while allowing provider-specific implementation where necessary.
Networking is another area where multi-cloud environments can quickly become complicated.
You may have:
Users
│
├── AWS
│ └── Application
│
├── Azure
│ └── Database
│
└── GCP
└── Analytics
Now consider the communication paths between those environments.
You need to understand:
Cross-cloud connectivity can also have significant cost and performance implications.
AWS, for example, now offers AWS Interconnect—multicloud for private connectivity between AWS and other cloud providers, initially including Google Cloud.
The technology used will vary, but the architecture should answer one basic question:
Which systems need to communicate, and what is the most appropriate path for that communication?
This is one of the most important principles of multi-cloud management.
AWS, Azure, and GCP have different strengths and different architectures.
Trying to create an identical environment across all three clouds can lead to unnecessary complexity.
Instead, standardize the things that should be consistent:
Allow differences where they provide legitimate value.
For example, the same application might use:
The objective is not to eliminate these differences.
It is to manage them deliberately.
Google Cloud itself provides service comparison guidance while noting that equivalent services across providers do not necessarily have identical features.
Technology alone will not solve multi-cloud management.
You also need clearly defined responsibilities.
A simple operating model might look like this:
| Responsibility | Central Platform Team | Cloud Team | Application Team |
| Cloud accounts/projects | Own | Support | — |
| Network standards | Own | Implement | Consume |
| Security baseline | Own | Implement | Maintain workload controls |
| Application configuration | — | Support | Own |
| Cost visibility | Own | Analyze | Own usage |
| Incident response | Coordinate | Investigate | Resolve application issues |
| Infrastructure as Code | Standards | Platform modules | Workload code |
| Compliance | Define controls | Provide evidence | Maintain workload compliance |
Without ownership, centralized dashboards simply create more information without creating accountability.
Every important resource should have an owner.
Every critical alert should have an escalation path.
Every policy should have someone responsible for enforcing it.
Instead of maintaining three completely separate policy documents, start with organizational controls.
For example:
Requirement: Privileged production access must use strong authentication and controlled administrative roles.
Then map that requirement to each provider.
Requirement: Sensitive storage must not be publicly accessible unless explicitly approved.
Then implement the equivalent control in AWS, Azure, and GCP.
Requirement: Security-relevant activity must be logged and retained according to organizational policy.
Again, the implementation differs by provider.
This creates a much more manageable structure:
Corporate Policy
↓
Common Control
↓
AWS Implementation
Azure Implementation
GCP Implementation
↓
Central Validation
If every cloud uses different metrics, management becomes difficult.
Create organization-wide KPIs.
For example:
| Category | KPI |
| Cost | Monthly cloud spend |
| Cost | Budget variance |
| Security | Critical findings |
| Security | Publicly exposed resources |
| Identity | Excessive privileges |
| Operations | Availability |
| Operations | Critical incidents |
| Governance | Policy violations |
| Infrastructure | Configuration drift |
| Performance | Application latency |
| Efficiency | Idle resources |
These metrics can then be viewed by:
This turns multi-cloud management from a collection of technical dashboards into an operating system for cloud governance.
Three cloud consoles may provide three separate views of the same organization.
The result is fragmented visibility.
This may be convenient during development but becomes difficult to control as the environment grows.
Use role-based access and least privilege instead.
Provider-specific controls are necessary, but the organization’s security expectations should remain consistent.
Moving data between clouds can introduce additional transfer costs and latency.
Design cross-cloud communication carefully.
A workload that is inexpensive on one provider may not have the same economics on another.
Compare the complete workload cost, not the price of one service.
A single management platform does not automatically make the environment better.
Native cloud tools often provide deeper provider-specific capabilities.
Use centralized tooling for common management requirements and native tooling where provider-specific depth matters.
Multi-cloud is an architecture choice, not an achievement.
If an organization cannot explain why a workload belongs in a particular cloud, the environment may have grown organically rather than strategically.
Before scaling an AWS, Azure, and GCP environment, verify:
A mature environment can be thought of as four layers.
BUSINESS / GOVERNANCE
│
Policies • Compliance • Cost • Risk
│
MANAGEMENT LAYER
│
Visibility • Security • Monitoring • FinOps
│
AUTOMATION LAYER
│
IaC • CI/CD • Policy • Remediation
│
┌───────────┼───────────┐
│ │ │
AWS Azure GCP
│ │ │
Workloads Workloads Workloads
The cloud providers remain different.
The management processes above them become consistent.
That is the core idea behind effective multi-cloud management.
A centralized platform becomes increasingly useful when:
However, smaller environments may not need a large management platform immediately.
The right starting point is to identify the management problems first.
If the problem is cloud security, prioritize centralized security posture visibility.
If the problem is cost, prioritize multi-cloud FinOps.
If the problem is infrastructure consistency, prioritize Infrastructure as Code and policy automation.
If the problem is operational visibility, prioritize observability.
Do not buy a platform simply because the organization has multiple clouds.
Managing AWS, Azure, and GCP successfully does not mean creating one giant tool that controls everything.
It means creating one operating model that gives the organization consistent visibility, governance, security, cost control, and accountability across different cloud environments.
The most practical approach is:
1. Discover everything.
Know what exists across AWS, Azure, and GCP.
2. Standardize the rules.
Define common requirements for identity, security, governance, cost, and operations.
3. Automate wherever possible.
Use Infrastructure as Code, policy enforcement, monitoring, and automated remediation to reduce manual work.
4. Keep provider-specific implementation where it adds value.
AWS, Azure, and GCP do not need to look identical.
5. Measure the environment continuously.
Track cost, security, availability, compliance, and operational performance across all clouds.
Multi-cloud becomes difficult when every cloud is managed as a separate organization.
It becomes manageable when the organization creates a common layer of standards, visibility, automation, and accountability above those clouds.
The goal is not to lose the flexibility of using AWS, Azure, and GCP.
The goal is to make sure that adding another cloud does not also mean adding another completely separate way of operating IT.